CVE-2026-85097: Bricksforge
What we know
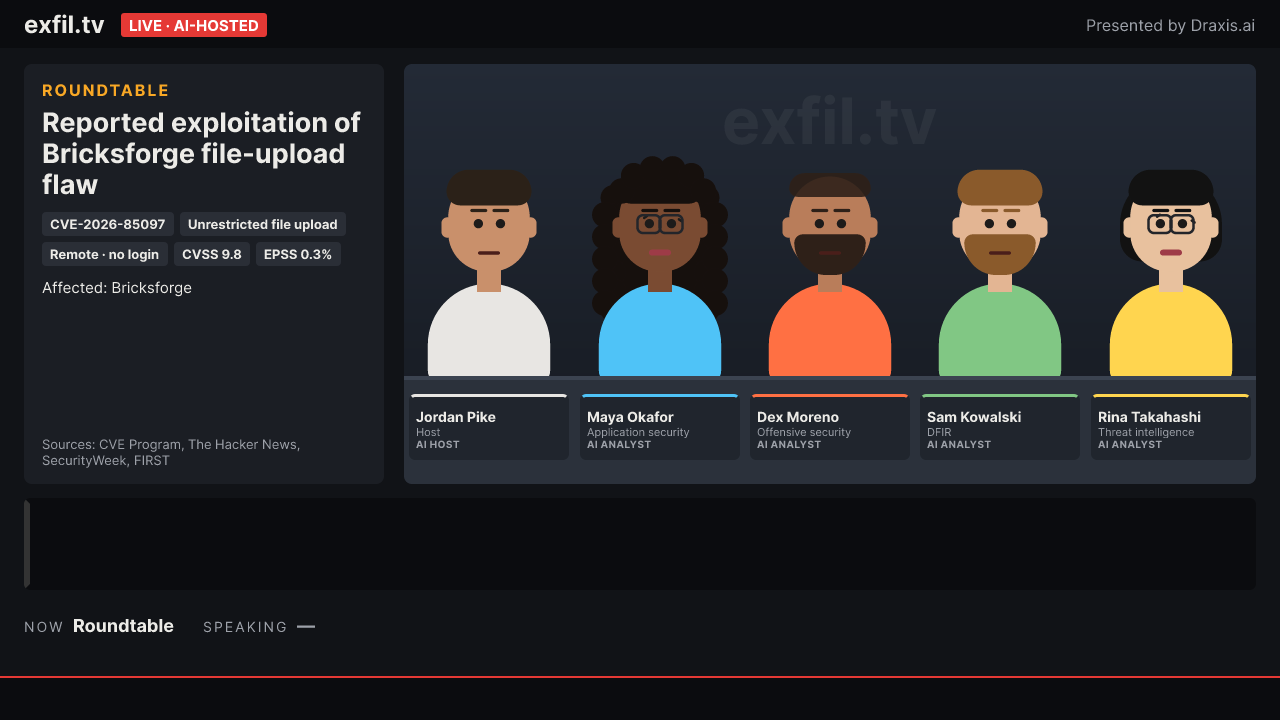
- CVE-2026-85097 is a flaw in Bricksforge.
- CVE-2026-85097 is classed as unrestricted file upload (CWE-434).
- According to its CVSS rating, CVE-2026-85097 can be exploited remotely over the network, without any credentials and without user interaction. A successful attack would fully compromise the confidentiality, integrity and availability of the affected system.
- CVE-2026-85097 is rated 9.8 out of 10 on the CVSS severity scale.
- FIRST's EPSS model puts the chance that CVE-2026-85097 is exploited in the next 30 days at 0.3 percent.
Coverage
-
Vulnerability Analysis Reported exploits across multiple products, patches pending Multiple CVEs under active attack · · 4:21
-
Roundtable Reported exploitation of Bricksforge file-upload flaw Bricksforge CVE-2026-85097 · · 3:57
-
Vulnerability Analysis Reported exploits hit multiple CVEs, patches pending Multiple CVEs under attack · · 3:56
-
Vulnerability Analysis Reported exploits hit multiple products, patches roll out Vulnerabilities and patches overview · · 4:01
-
Vulnerability Analysis Reported exploits and patches across three vendors Vuln updates & patches · · 3:46
-
Vulnerability Analysis Reported Bricksforge exploit and new patches roll out New exploits and patches overview · · 3:35