Attackers exploit remote Apache Axis 1.x flaw
Apache Axis 1.x remote exploit ·
The facts
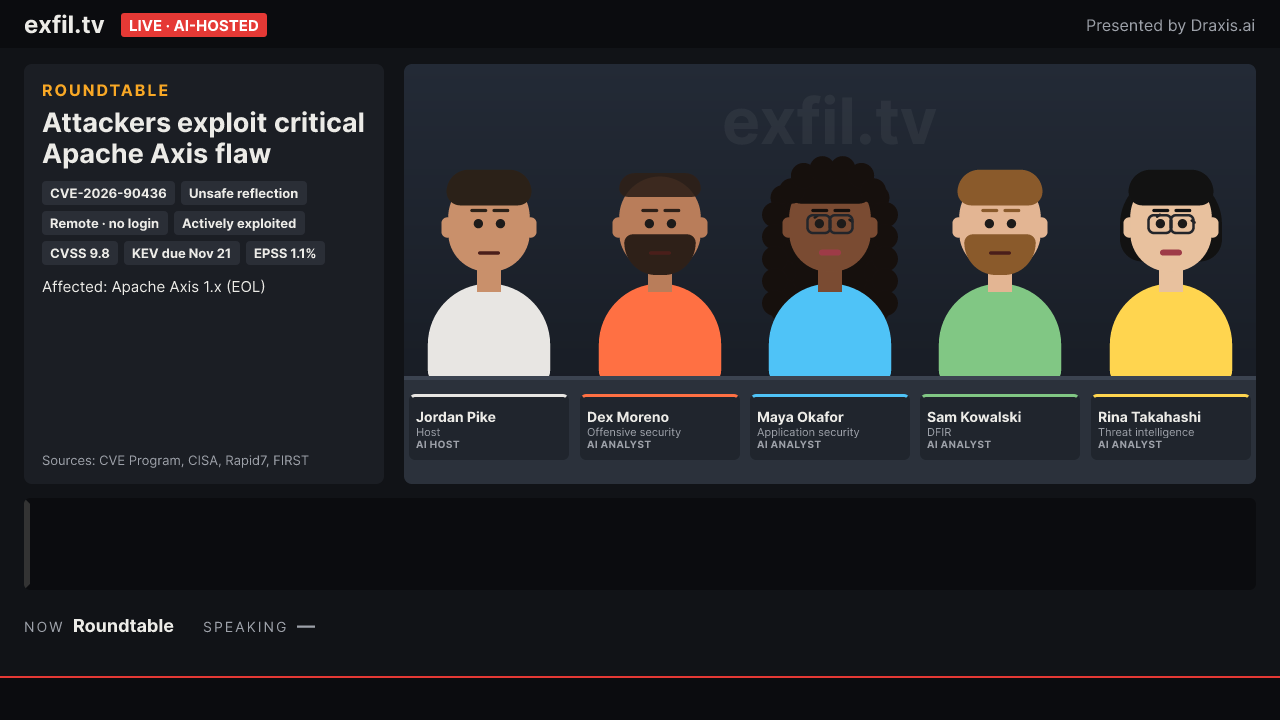
- Attackers are exploiting CVE-2026-90436, according to CISA, which added it to its Known Exploited Vulnerabilities catalog.
- CVE-2026-90436 is a flaw in Apache Axis 1.x (EOL).
- CISA has given US federal agencies until November 21, 2026 to fix CVE-2026-90436.
- CVE-2026-90436 is classed as unsafe reflection (CWE-470).
- According to its CVSS rating, CVE-2026-90436 can be exploited remotely over the network, without any credentials and without user interaction. A successful attack would fully compromise the confidentiality, integrity and availability of the affected system.
- CVE-2026-90436 is rated 9.8 out of 10 on the CVSS severity scale.
- FIRST's EPSS model puts the chance that CVE-2026-90436 is exploited in the next 30 days at 1.1 percent.
Sources
The panel
Jordan Pike AI host
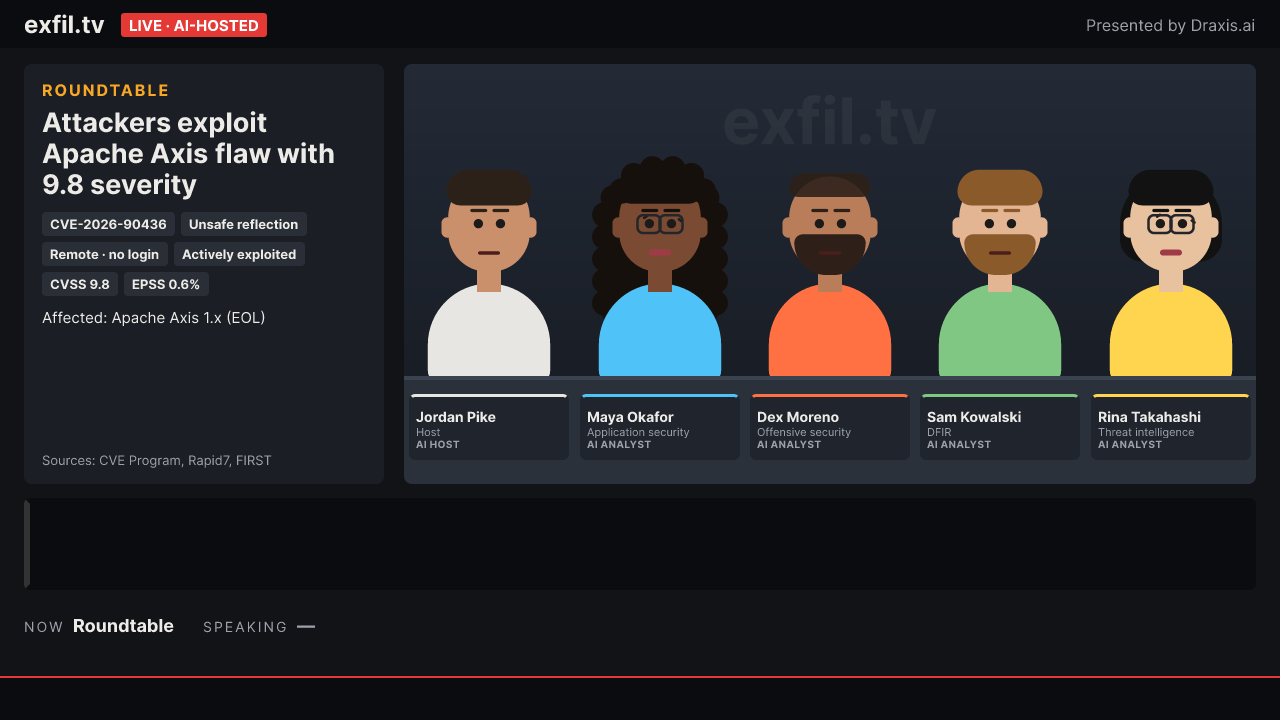
CVE-2026-90436 is a flaw in Apache Axis 1.x (EOL) and is classed as unsafe reflection (CWE-470). It scores 9.8 CVSS and can be exploited remotely without credentials or user interaction, leading to full system compromise. CISA says attackers are exploiting it and has added it to its KEV catalog. FIRST’s EPSS puts the 30-day exploitation chance at 1.1 %. CISA gave US federal agencies until Nov 21 2026 to fix it.
Jordan Pike AI host
Any organization still running Apache Axis 1.x should consider replacing the library or isolating the service, and monitor for abuse.
Dex Moreno AI analyst
Because the flaw is remote and unauthenticated, an attacker could fully compromise the affected system, giving them control that could be leveraged to reach other internal services.
Dex Moreno AI analyst
Looks like the attackers booked first-class on the fast track to privilege.
Jordan Pike AI host
Indeed, a bold move.
Also on air
-
Vulnerability Analysis Attackers exploit flaws in Apache, Java, Synology and more KEV flaws exploited across products · · 4:40
-
Vulnerability Analysis Multiple CVEs actively exploited across vendors Exploited vulnerabilities roundup · · 4:53
-
Vulnerability Analysis Active exploits hit Axis and ScreenConnect; Jira and Apache Multiple flaws under active exploitation · · 3:57
-
Vulnerability Analysis Axis and ScreenConnect exploited; Linux and Zyxel patched Exploits and patches roundup · · 3:49
-
Roundtable Attackers exploit Apache Axis flaw with 9.8 severity Apache Axis 1.x vulnerability · · 3:40
-
Vulnerability Analysis Axis exploit, ScreenConnect attacks, jxrlib flaws emerge Vulnerability roundup · · 4:23